Editorial

Expensive Fraud Calls

Published on:

October 20, 2014

The recent case of phone call fraud highlights the growing risk of PBX systems being compromised, with hackers using them to dial expensive numbers. This situation often arises when the PBX is used as a "least cost router" to route calls through expensive destinations. Even without external voice traffic, however, bots on local networks can exploit PBX systems by accessing the TAPI feature and dialing numbers directly from a computer. To mitigate risks, it's crucial to ensure strong security measures, like checking for viruses, using secure passwords, and verifying the fraud detection features offered by service providers. It's also important to restrict expensive number calls via the PBX dial plan and ensure TAPI licenses are carefully managed.

It happened again, and it won't be the last time: http://finance.yahoo.com/news/phone-hackers-dial-redial-steal-012343295.html. Another victim of phone call fraud, the result of a hacked PBX somehow accessible to the bad guys.

We have talked about it before, but reading the article I think it's important to discuss some points that weren't so clear before. The first one is some carriers really seem to go after the money, even if they have to go to court. In contrast with the credit card industry, fraud calls are the responsibility of the customer, not the provider.

The next point is it's obviously not necessary the PBX actually receives voice traffic from the public internet - fraud calls typically fraud uses the victim's PBX as a kind of “least cost router” for terminating traffic into expensive countries. But when calling expensive 900 numbers, like those mentioned in the article, there's no need to have any traffic with the outside world. All it takes is the PBX using its route into the PSTN world.

In theory, a bot on a computer in the LAN can use the click-to-dial feature of the PBX to keep on dialing expensive numbers. The voice would end up somewhere either on the local PC or smart phone, or just on the phone on the office table. On the weekend, when nobody is in the office, it would take some time to figure out what's going on.

This is new. If a bot can access the local TAPI on the computer and initiate a call, you're in trouble. There's no extra password check between the TAPI client and the TAPI server. All it takes is a program running on the local PC that starts to dial numbers.

So what are we learning from all of this?

Apart from the usual recommendations to check for viruses on your computer and make sure users are choosing strong passwords and PIN codes, you should check if your service provider has a fraud detection feature. This will limit the damage, in case you get hacked for whatever reason, despite all the precautions you took. If you are using prepaid accounts, the damage will be limited to the money you've put into the meter.

By default, version 5 doesn't come with a CSTA license, which is required for TAPI calls. If you have the license and are using TAPI, you can take a few measures that reduce exposure to the risk - you can double check what numbers can be called from your PBX in the dial plan. In many cases, it's not necessary that PBX users are dialing expensive hotlines; if they do, you can set the flag in the dial plan so they have to enter a PIN code. And you can make sure PCs are turned off when users aren't in the office. This makes sure you don’t have any surprises on your phone bill on Monday morning. It also saves power.

Latest Articles

View All

AI Voice Agents and Business Calls: A Practical Compliance Checklist

AI-powered calling gives businesses new ways to manage conversations, improve availability, and respond to callers more efficiently. It also introduces important questions about transparency, consent, privacy, data handling, and accountability. Organizations need clearly defined boundaries for what a Voice Agent may answer, which systems it can access, and when identity verification or human assistance is required. A thoughtful deployment balances automation with appropriate safeguards, helping businesses use conversational AI confidently while protecting callers and maintaining trust.

September 23, 2026

Vodia Podcast: How Brandywine Built a Multimillion-Dollar Business with Vodia

Yori Kasprzak, founder of Brandywine Technical Partners, joins Vodia’s Eric Altman to share how he built a multimillion-dollar business and the role Vodia has played in its growth. From cloud telephony and CRM integrations to door systems, AI and mobile workforces, he explains how Brandywine solves customer challenges with Vodia’s open platform and shares advice for partners looking to grow. His story shows how finding customer pain points can create business opportunities beyond traditional phone services.

September 17, 2026

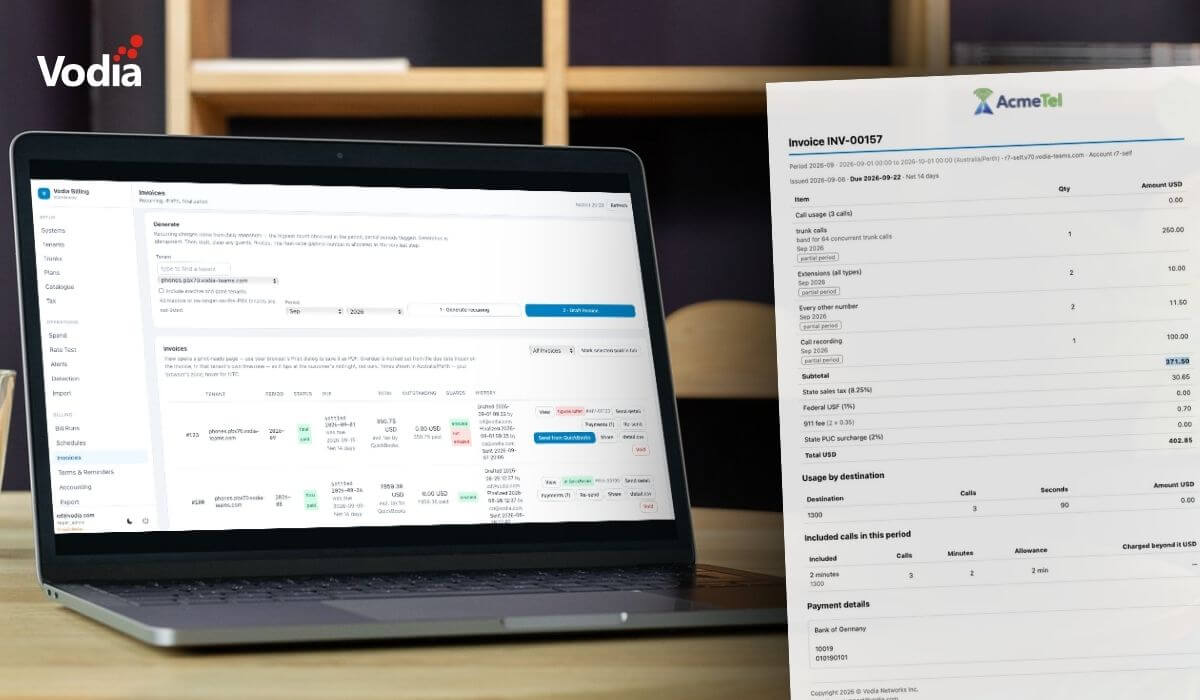
Turn PBX Activity Into Customer Invoices with Vodia Billing

Vodia Billing turns PBX activity into customer invoices by bringing call rating, recurring charges, taxes, invoice generation and payment tracking into one dedicated platform. Built for Vodia PBX fleets, it can process CDRs, count recurring PBX items, produce branded invoices, connect with Xero and QuickBooks Online, monitor overdue payments and flag potential fraud. It also gives MSPs clearer visibility into margins, helping them understand not only what customers owe, but what their services are actually costing to deliver.

September 15, 2026